Why a secure portal beats email and shared folders
Email and shared cloud folders are insecure by default for client work. Email is plaintext between mail servers, attachments are easy to forward to the wrong person, and once a document is in someone's inbox you have lost control of it. Shared folders are easy to over-share, hard to audit and rarely have project-scoped permissions. Both leave you with no real record of who accessed what, when.
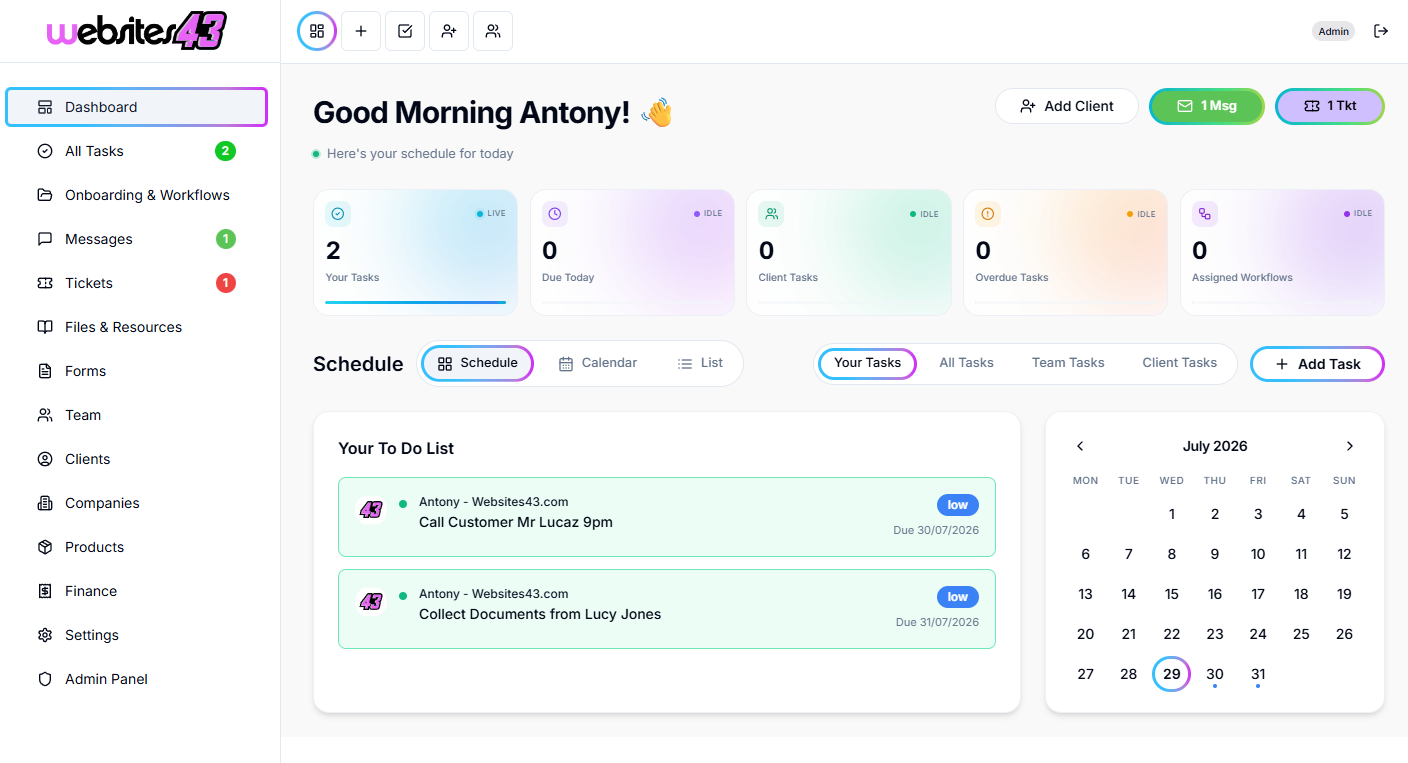
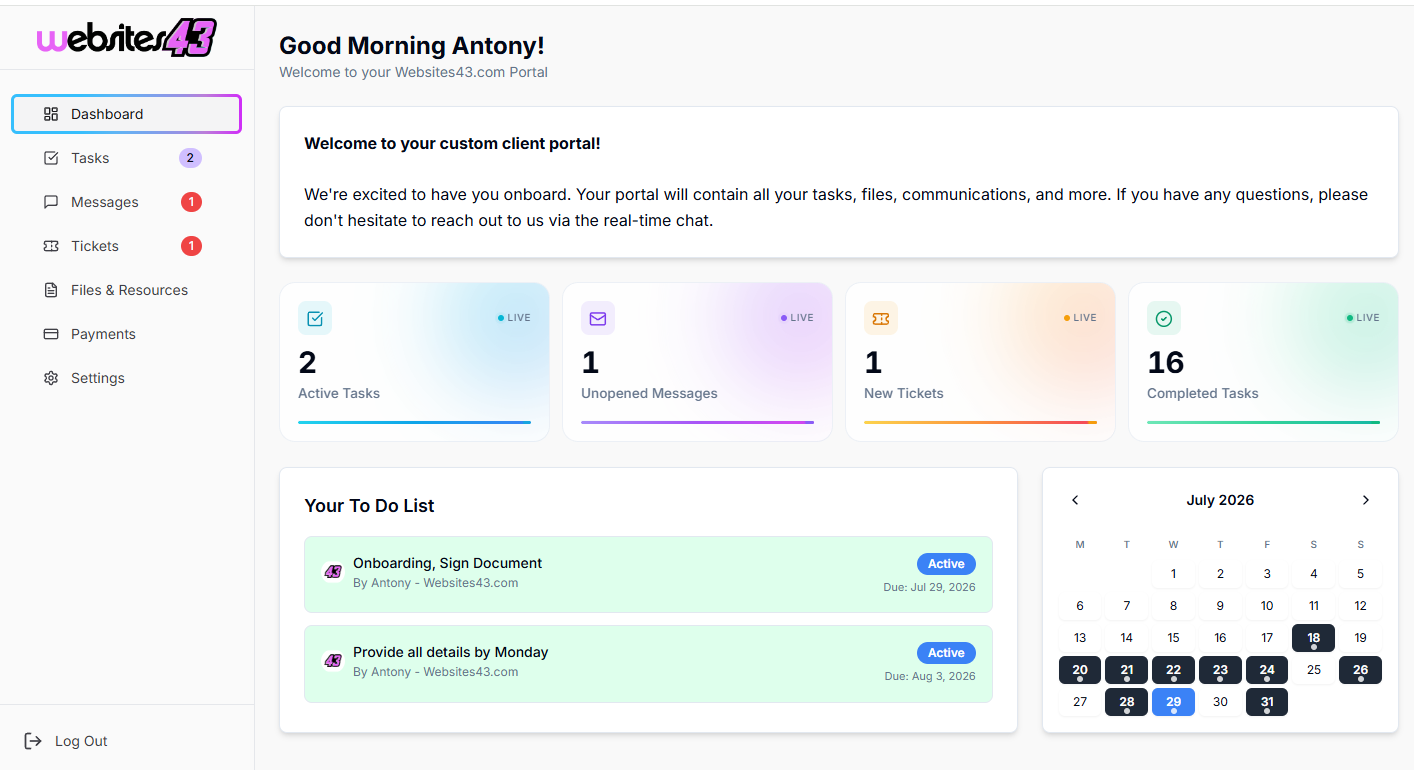
A secure client portal centralises sensitive data in one controlled environment. Access requires authentication. Permissions are scoped per project and per role. Every view, download and signature is logged. Sharing is intentional, not accidental. Revocation is one click, not a frantic email chain. The compliance answer to "where does our client data live and who can see it?" becomes a single sentence instead of a paragraph of caveats.
- Encrypted transport (TLS) on every connection
- Encrypted storage of files at rest
- Role-based access control across internal users
- Project-scoped access for client users — one client never sees another's data
- Magic-link authentication with configurable session expiry
- Full audit log of every action, viewable and exportable